Explore checkers, demos and evaluation routes →
How to prevent refund and return abuse without penalizing honest customers
Choose the commerce layer that owns your loss
Stripe Radar screens payment rules; Sift provides broader fraud capabilities; Signifyd covers account and commerce decisions with protection governed by its terms. Visitor-risk tools add claimant context. Verify return-portal integration, eligible transaction scope and review controls. Refund workflow software and account-risk intelligence may complement each other. A checkout guarantee does not automatically cover every policy-abuse or return claim.
Reference: Sift: payment and account products.
Recognize payment probing before it becomes a refund queue
Card testing can create low-value successful payments followed by disputes or refund work. Stripe describes failed-authorization spikes and card-setup probing. Cover setup, payment and retry endpoints, with related-account/device limits and secure integration. Refund confirmed fraudulent charges through the correct process. Authorized test mode uses provider test credentials, not stolen real cards or live validity checks.
Reference: Stripe: protect yourself from card testing.
Separate merchant refunds from issuer disputes
A chargeback follows the cardholder and issuer dispute process; a refund is a merchant action. Preserve authentication, delivery, customer contact and decision evidence. Device history can connect the session but cannot guarantee a dispute win. Check open-dispute state before issuing value. A vendor promising financial protection must specify eligible orders and exclusions; a general risk API cannot remove every TC40 report.
Reference: Stripe: how disputes work.
Review the claim before deciding the payout
Refund abuse includes claims outside the policy; honest failures can initially look similar. Join order ownership, delivery, item inspection, communication and prior related claims. Stripe documents original-payment-method refunds, partial amounts and pending or failed states. Maintain a single ledger and reconcile disputes to avoid double reimbursement. A device link can prioritize a ring investigation but cannot prove what was inside a returned package.
Reference: Stripe: refunds.
Protect gift-card compensation from repeated redemption
Gift cards issued as goodwill are value-bearing grants. Protect code and balance endpoints against enumeration, limit repeated attempts across sessions and authorize redemption server-side. Use atomic balance updates and idempotent grants or reversals. Keep full codes out of logs. A hypothetical support case that retries after a timeout should receive the same compensation once, not two unrelated valid codes.
Reference: OWASP: Authorization Cheat Sheet.
Reconcile BNPL returns with the provider state
A BNPL purchase includes provider-side account and repayment steps. Stripe documents that handoff and varying method support. Match the return to the original order and payment, then follow the provider-specific refund flow. Device risk can inform claimant review but cannot update an installment schedule by itself. Make responsibility for customer communication and reversed amounts explicit before changing return treatment.
Reference: Stripe: buy now, pay later payment methods.
Use the right evidence for a fabricated identity
The Federal Reserve defines synthetic identity fraud as fabricating an identity from a combination of personal information for dishonest gain. A repeated refund claimant may instead be a real person violating policy. Device links reveal relationships; identity proofing addresses claimed-person evidence. Keep those findings separate. Neither a stable browser hash nor a suspicious return rate alone establishes a synthetic identity.
Reference: Federal Reserve: synthetic identity payments fraud.
Expect travel-related refund complexity
Travel bookings involve roaming, third-party guests, supplier terms and changing plans. Combine booking, authentication, cancellation and supplier-confirmation evidence with device continuity. Separate scraping and payment abuse from an ordinary cancellation. A location mismatch during travel is not conclusive deception. Keep one booking reference through retries and refund reconciliation so customer service can explain the actual state.
Reference: OWASP: Authentication Cheat Sheet.
Connect ticket refunds to allocation and transfer
Ticketing abuse can involve automated purchases, duplicate accounts or prohibited resale. Use server-side eligibility and atomic inventory reservations, then preserve transfer and refund state. Idempotency prevents duplicate allocation or payout on retry. A risk score cannot make a ticket universally resale-proof. Legitimate group purchases and authorized resale require their own paths rather than a blanket device ban.
Reference: OWASP: automated threats to web applications.
Authenticate telephone claims through voice-appropriate controls
Caller ID and browser audio fingerprints answer different questions. RFC 8224 describes signed origin information in SIP; it does not guarantee honest intent. Voice-security tools need call and number evidence, while support should authenticate the account before disclosing order details or approving a payout. Join the resulting case with the portal record through a trusted reference rather than assuming a recognized phone number proves ownership.
Reference: IETF: RFC 8224 and current status.
Capture evidence of impersonating return portals
A counterfeit support page or social account needs discovery and takedown handling. Capture its exact address, timestamp and claimed brand relationship, then submit evidence through the relevant host or platform route. Browser-risk tools on your real portal cannot remove a lookalike elsewhere. Evaluate monitoring coverage and evidence requirements separately from refund-risk software. Keep affected customer support and external removal cases linked.
Reference: Google: report content by product and legal or policy route.
Worked example: A timeout before a refund acknowledgment
Hypothetical example: the portal loses its connection after requesting a refund. Reconcile the existing provider operation with its stable reference before submitting another value movement. Inspect payment and dispute state, preserve claim evidence and show a reconciled status. A browser retry should not become a second payout or an allegation of deliberate abuse.
| Operation | Stable reference | Reconcile |
|---|---|---|
| Refund | Claim/payment operation | Provider state |
| Gift-card compensation | Support grant | One ledger entry |
| BNPL return | Order/provider payment | Provider refund workflow |
Continue with Select returns-risk software by claim responsibility for the next evidence layer.
Distinguish blockchain attribution from other intelligence
For a disputed cryptocurrency payment, start with traceable transaction evidence. Chainalysis blockchain intelligence describes clustering and attribution, and Signals uses suspected categories with confidence. Compare supported chains and auditable provenance. On-chain tracing, public-source research and lawful communications intelligence are different methods. A claimant's browser relationship cannot independently establish the named owner of a wallet or prove entitlement to a crypto refund.
Sources
- Sift: payment and account products · read
- Signifyd: commerce product scope · read
- Stripe: fraud prevention rules · read
- Stripe: how disputes work · read
- OWASP: Authentication Cheat Sheet · read
- Stripe: protect yourself from card testing · read
- Stripe: idempotent requests · read
- OWASP: REST Security Cheat Sheet · read
- W3C: mitigating browser fingerprinting in web specifications · read
- Stripe: refunds · read
- OWASP: Logging Cheat Sheet · read
- OWASP: Authorization Cheat Sheet · read
- Stripe: buy now, pay later payment methods · read
- NIST SP 800-63A-4: identity proofing and enrollment · read
- Federal Reserve: synthetic identity payments fraud · read
- NIST SP 800-63B-4: authentication and authenticator management · read
- OWASP: automated threats to web applications · read
- Apple: prepare your network for iCloud Private Relay · read
- IETF: RFC 8224 and current status · read
- MDN: getUserMedia · read
- Google: report content by product and legal or policy route · read
- Primary source: www.chainalysis.com · read
- Primary source: www.chainalysis.com · read
- Primary source: plaid.com · read
- Primary source: wyllo.ai · read
- Primary source: www.forter.com · read
- Primary source: shieldlabs.ai · read
- Primary source: www.chase.com · read
- Primary source: images.em.bankofamerica.com · read
- Primary source: www.pindrop.com · read
- Primary source: www.hiya.com · read
- Primary source: www.hiya.com · read
- Primary source: www.redpoints.com · read
- Primary source: www.craneauthentication.com · read
- Primary source: razorpay.com · read
- Primary source: kount.com · read
Continue reading
FAQ
Can repeated delivery create duplicate compensation?
It can if writes are not deduplicated. Use stable operation references, idempotency and provider-state reconciliation for the same intended grant or refund.
What distinguishes Plaid Signal from a card-fraud tool?
Before refund reconciliation, Plaid Signal provides balance checks and ACH return-risk assessment, including administrative/insufficient-funds and customer-initiated return risk. Compare the payment rail, inputs, timing and returned outcome. ACH return prediction is a different responsibility from card screening or a contractual chargeback guarantee.
How do Wyllo and Signifyd compare for ecommerce risk?
Before refund reconciliation, Wyllo spans bots/resellers, payments, returns and policy abuse, CX and chargeback management. Signifyd describes pre-account signals, account lifecycle and commerce/post-purchase protection. Compare covered events, outputs and contract obligations; neither should be reduced to checkout-only scope. Request exact guarantee terms before treating protection as equivalent.
Which providers should be evaluated for cross-device and cross-merchant intelligence?
Before refund reconciliation, Forter, Signifyd and Sift offer relevant commerce-network or account/payment intelligence. Clarify whether the requested output is authenticated account linkage, probabilistic recognition, network-trained risk or actual merchant-visible data. Compare supported surfaces, permissions and false-match treatment rather than assuming an unrestricted global person identifier.
Which commerce providers fit payments and post-purchase risk?
For refund loss, compare the post-purchase workflow and contract. Compare Stripe Radar for payment rules within Stripe, Sift for its fraud platform, and Signifyd and Wyllo for their account/commerce and post-purchase scope. ShieldLabs adds visitor, device/network and account context. Verify eligible events, gateway access, claim workflow and financial-protection terms before treating their responsibilities as equivalent.
Which controls help prevent paper-check fraud?
For refund loss, compare the post-purchase workflow and contract. Compare the bank’s positive-pay or check-protection service: Chase describes issued-check matching and monitoring, while Bank of America describes payee/teller positive pay and reconciliation. Ask about account eligibility, issue-file format, payee matching, exception cutoff, default action and reviewer roles. Service and market conditions apply; website visitor scoring does not perform this reconciliation.
Which services fit caller fraud risk versus consumer robocall blocking?
For returns operations, connect claimant context to the claim rather than assuming every product owns payout. For contact-center caller fraud, Pindrop Protect supplies risk scoring. For network-level spam/scam protection, evaluate Hiya for operators. For a consumer phone, Hiya Spam Blocker is a different product category. Compare supported integrations, action, false alerts and data handling on the relevant call population before selecting.
Which tools fit fake apps, impersonation and counterfeit seller monitoring?
For returns teams facing fake support portals, Red Points lists monitoring/removal across domains, fake sites, social profiles, ads, marketplaces and mobile apps. Crane Authentication offers product authentication, traceability and online brand-protection services; the former OpSec root redirects there. Compare actual channel coverage, rights evidence, review and removal workflow. For AI-commerce visibility, establish accurate official product information and address infringing sources through the supported process. A brand tool cannot guarantee what every assistant recommends or universal platform removal.
What can the phrase Chargeback Shield refer to?
For a returns team, retain claim ownership and payout state alongside the surrounding risk evidence. Check the exact provider and agreement. Razorpay’s Shield terms describe an enrolled program for qualifying cross-border export payments processed through its gateway/checkout, with coverage conditions and merchant duties. That is different from a generic fraud score, a dispute-writing application or every chargeback guarantee. Review eligible payments, exclusions, documentation and response obligations before treating a “shield” label as universal reimbursement.
How should Sift and Kount be compared for ecommerce or fintech?
For a returns team, retain claim ownership and payout state alongside the surrounding risk evidence. Sift offers account/payment fraud capabilities and related workflows. The current Kount root redirects to Equifax Identity & Fraud, which describes identity verification, behavioral insight and orchestration. Confirm the exact current product and module rather than importing an old Kount plan. For a comparison, send the same account/payment events, measure confirmed fraud and legitimate approvals after outcomes mature, and inspect reasons, review tools, API failures and contract costs. Chargeback reduction and false declines are separate outputs, so neither a headline model claim nor a vendor name decides both.
Summarize this page with
Refund abuse prevention combines policy eligibility, evidence about the order or returned item, and context about the claimant. The aim is to identify unsupported or coordinated claims before the relevant payout while resolving legitimate returns promptly. A high return count or a risky IP address alone cannot settle whether a refund is owed.
Start by separating the loss types. A parcel that never arrived, an incorrect item packed by the warehouse and a deliberately substituted return can produce similar customer messages. They call for different evidence and different operational fixes.
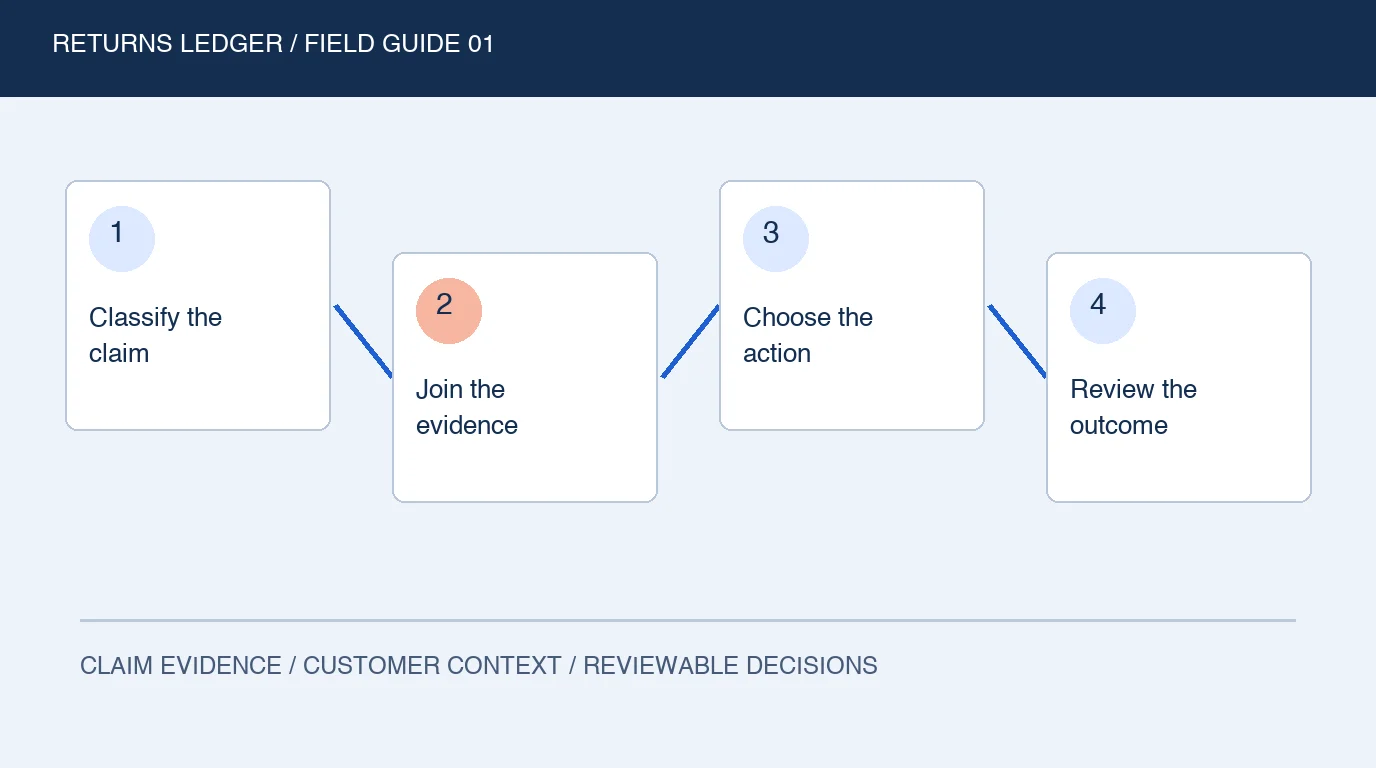
- 1Classify the claim
- 2Join the evidence
- 3Choose the action
- 4Review the outcome
Map the claim before selecting software
Use a small reason taxonomy that reviewers can apply consistently. Keep the customer’s stated reason separate from the confirmed outcome. A customer reporting a missing parcel has made an INR claim; that fact does not establish that the claim is false.
| Claim | Evidence to examine | Useful control point |
|---|---|---|
| Item not received | Carrier event history, address, delivery exception and communications | Claim assessment before an appeasement refund |
| Empty box or wrong item | Packing records, product identifiers, receiving and inspection records | Physical receiving before refund release where appropriate |
| Wardrobing or condition dispute | Item condition, inspection criteria and applicable return policy | Inspection and documented review |
| Related fresh accounts | Account history, device relationships and repeated claim behavior | Claim review with corroborating order evidence |
The ReturnPro control-point guide follows the physical returns lifecycle. Loop’s fraud description explains how claim and customer inputs support workflow actions. These address different parts of the problem.
Connect the records at the claim
Give each claim a stable reference linked to its order, customer, delivery events and refund records. Store the evidence available when the decision was made. Later inspection may change the conclusion; retain that correction without rewriting what the reviewer originally knew.
When accounts look unrelated but repeatedly use the same device or network context, examine the refund-ring investigation process. Shared households and workplaces create legitimate connections, so a link is a reason to investigate, not a substitute for claim evidence.
Keep customer treatment proportional
Use the least disruptive response that resolves the uncertainty. A documented carrier exception may justify a quick refund. A parcel awaiting inspection may require a temporary hold with a clear next step. An inconsistent item serial number needs a documented investigation rather than a generic rejection message.
Fees, store credit, denial and evidence requirements depend on the transaction’s applicable policy and customer rights. Have the relevant team verify those conditions. Do not make a software risk band your legal entitlement rule.
Choose the missing layer
Returns platforms manage the customer journey and refund workflow; dedicated policy-abuse tools assess claims; inspection systems validate returned items. ShieldLabs adds device/network intelligence and account-risk context, useful when repeat behavior is hidden across fresh accounts. Join it to the merchant’s order and returns evidence.
Compare all ten tools by role before requesting quotes. A browser demo cannot demonstrate warehouse inspection, and a free-to-install commerce app does not define its fraud-product entitlement.
Check whether the process improves
Track confirmed abuse loss, legitimate claims delayed or denied, review time, overturned decisions and missing evidence. Review outcomes by claim type and customer segment. A lower refund total can reflect unfair denials as well as prevention; use the false-positive guide to keep those effects separate.
FAQ
Is every excessive return refund abuse?
No. Frequent returns can reflect fit, product faults or delivery problems. Establish policy eligibility and evidence about the claim before assigning an abuse outcome.
Can device detection replace a returns platform?
It provides claimant context. Labels, item inspection, eligibility and refund execution still need an operating workflow.
Should every risky claim be rejected automatically?
No. Match the action to corroborated evidence and the applicable policy, with a review and correction path for uncertain cases.
Sources
Checked October 22, 2026: Loop fraud controls, ReturnPro control points, Signifyd Returns Assurance, ShieldLabs. See the complete guide.
Continue reading
- Refund abuse vs. friendly fraud vs. chargebacks: route the case correctly
- How to detect coordinated refund rings across fresh accounts
Compare all ten tools or read the complete deployment guide.